ActiveMQ vulnerability in Armatura One: an exploited CVE reaches physical access control
The October 6th edition analyzes critical vulnerabilities affecting components close to physical operations. The main case is Armatura One, an access control platform that incorporates a vulnerable version of Apache ActiveMQ associated with active exploitation and ransomware campaigns. Also reviewed are ten flaws in Toptech TMS7 and TopHAT, a remote code execution in MikroTik RouterOS, and…
Editorial
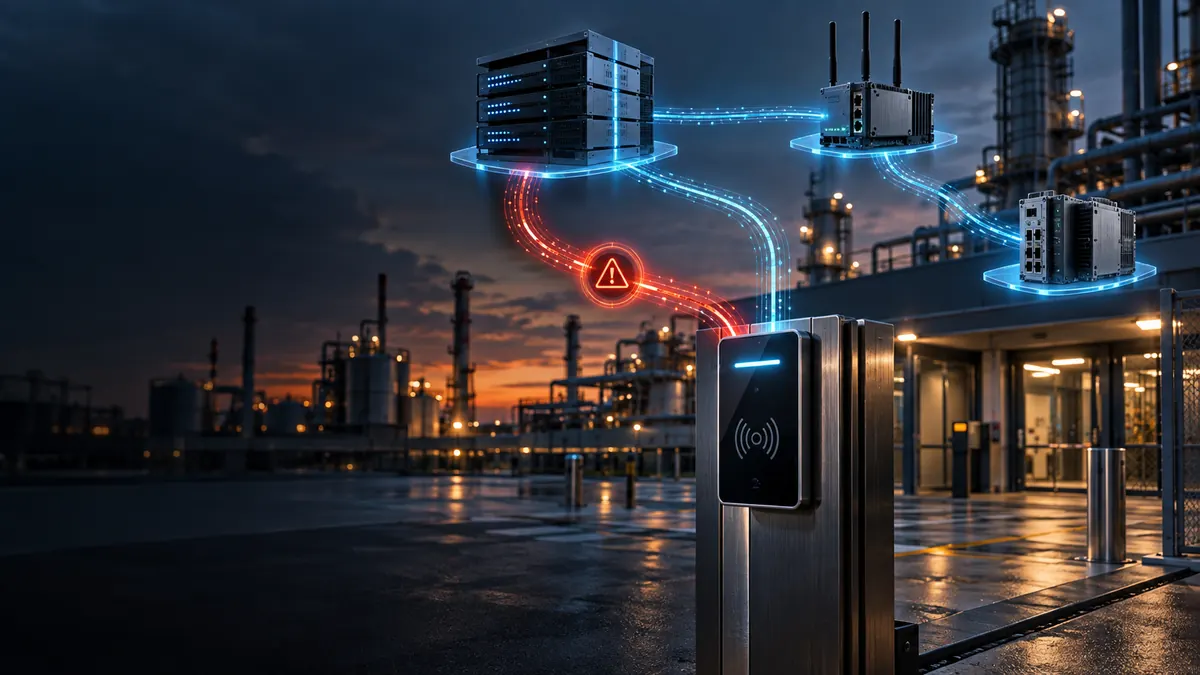
This week, CISA and INCIBE published over a dozen advisories. Three of them require immediate attention. The first involves Armatura One, a physical access control system with an embedded Apache ActiveMQ instance that has a 2023 vulnerability already listed in CISA’s KEV catalog and used in ransomware campaigns. The second affects the Toptech TMS7, a terminal management system found in hydrocarbon facilities. The third is MikroTik RouterOS, a router frequently found in industrial networks of all types. If any of these products are in your network, this edition is for you.
Vulnerabilities of the week
[CRITICAL] ActiveMQ vulnerable in Armatura One: an exploited CVE reaches physical access control
Armatura One is a physical access control management system used in manufacturing, energy, and transportation facilities. It embeds Apache ActiveMQ and exposes its OpenWire protocol listener to the network by default. The integrated version is vulnerable to CVE-2023-46604: a data deserialization flaw that allows an unauthenticated remote attacker to execute arbitrary code with the highest operating system privilege level before credentials are validated. CISA includes this CVE in its Known Exploited Vulnerabilities (KEV) catalog and links it to ransomware campaigns against Apache ActiveMQ installations. The same advisory documents hardcoded credentials for the database superuser (CVE-2026-94592), a fixed cryptographic key shared across installations to encrypt database credentials (CVE-2026-94591), database passwords logged in plaintext during backups (CVE-2026-94593), and broker credentials logged in plaintext during normal operation (CVE-2026-94594). The combination can facilitate full host compromise and credential reuse. In our experience, physical access control systems are rarely included in the scope of OT assessments and frequently share network segments with engineering workstations.
Suggested action: Verify if Armatura One is deployed in your organization. If the installed version is older than 4.7.2 (global line) or 4.6.1_USA (US line), update immediately. Confirm that the ActiveMQ OpenWire protocol port is not accessible from unauthorized segments. Audit log files, backups, and support packages for plaintext passwords; rotate any credentials that may have been exposed. Change the database superuser password if it was not done during installation. Contact official Armatura LLC support to obtain the update package.
All updates must be validated with the manufacturer beforehand, tested in a controlled environment, and executed in accordance with the organization’s change management process and maintenance windows.
[CRITICAL] Toptech TMS7 and TopHAT: ten flaws in a hydrocarbon terminal management system
Toptech TMS7 and its variant, TopHAT, are terminal management systems used in energy, chemical, and hydrocarbon transportation facilities. Version 7.6.3 contains ten vulnerabilities reported by Shell CyberDefence researchers. The most severe (CVE-2026-71379, CVSS 10.0) allows any unauthenticated attacker to export entire database tables with a single manipulated HTTP request. CVE-2026-70356 (CVSS 9.1) allows for the uploading and execution of arbitrary PHP files on the web server. Five interface entry points are vulnerable to time-based blind SQL injection (a type of security vulnerability where an SQL injection attack occurs, but the web application does not display query results or database errors in HTTP responses) (CVE-2026-72510, CVE-2026-63713, CVE-2026-68954, CVE-2026-68068, CVE-2026-72507). Additionally, the application does not regenerate the session identifier after authentication, which enables session fixation attacks to take control of active accounts (CVE-2026-71302). In our experience, TMS systems for storage and dispatch terminals are often connected to corporate networks for ERP integration, which significantly amplifies the impact radius of these flaws.
Suggested action: Update to version 7.8, available on the Toptech Systems security blog. If an immediate update is not possible, ensure that the TMS web interface is not accessible from unauthorized networks or the internet. Review access logs for anomalous POST requests to the export endpoint. Consider implementing a WAF as a temporary compensating control.
All updates must be validated with the manufacturer beforehand, tested in a controlled environment, and executed in accordance with the organization’s change management process and maintenance windows.
[CRITICAL] Moxa MGate protocol gateways: stack overflow and compromised firmware verification
Moxa MGate MB3000 and MGate 5000 series protocol gateways contain two vulnerabilities published this week by INCIBE-CERT (INCIBE-2026-698). CVE-2026-86325 (critical severity) is a stack-based buffer overflow in the account management interface: an authenticated user with read-only permissions can send a manipulated account name to access credentials in memory, modify device content, or cause a denial of service. CVE-2026-86326 (high severity) affects the firmware update mechanism: the cryptographic signature verification is incorrect, allowing an attacker with access to the update interface to install a modified image that survives subsequent updates. In our experience, MGate gateways frequently appear in industrial installations as bridges between Modbus RTU/TCP, BACnet, DNP3, and Ethernet networks in the manufacturing, energy, and water sectors. There is no fix available for CVE-2026-86326; Moxa recommends obtaining firmware only from official sources and applying the hardening guides for the MB3000 and 5000 series.
View INCIBE advisory →
View manufacturer advisory →
Suggested action: For CVE-2026-86325, apply the corrected firmware versions (MGate MB3170/MB3270 → 4.7.1; MB3180 → 2.7.1; MB3280 → 4.6.3; MB3480 → 4.5.1; MB3660 → 3.4.5; MGate 5217 → 1.5.5) by requesting them from Moxa technical support. For CVE-2026-86326, as long as no fix exists, ensure the firmware update interface is not accessible from unauthorized networks, and verify the integrity and origin of the firmware before any update. Apply physical and logical access controls to the administration consoles of the affected equipment.
All updates must be validated with the manufacturer beforehand, tested in a controlled environment, and executed in accordance with the organization’s change management process and maintenance windows.
In brief
- ABB PCM600 ≤ 2.14: The task scheduler service runs as LocalSystem but can be controlled by standard users in the local group, which enables local privilege escalation; additionally, project file extraction does not validate paths and allows writing outside the intended directory. For CVE-2026-15953, ABB released hotfix 2.14 Hotfix 20260923. For CVE-2026-15952, there is no fix available, and the configuration mitigations indicated by ABB must be applied. (CVE-2026-15952, CVE-2026-15953 — ICSA-26-274-03)
- WAGO PLCs and controllers (firmware <4.8.9): Unauthenticated path traversal in the dynamic creation of BACnet File Objects allows for reading or overwriting arbitrary files and potentially fully compromising the device (CVE-2025-41753, critical). Update to firmware 4.8.9 (FW30) or later; for custom firmware, request the corrected version from WAGO. (INCIBE-2026-688)
- CODESYS (versions <3.5.22.40 on Windows products / <4.23.0.0 on Linux products): A race condition in CmpMonitor2 and unbounded resource allocation in Gateway Client can lead to denial of service or memory corruption. Version 4.23.0.0 for Linux products is scheduled for the fourth quarter of 2026. (CVE-2026-79625, CVE-2026-76992 — INCIBE-2026-684)
- Johnson Controls EasyIO Neo Series EC and CW: Transmission of credentials and session data in cleartext via HTTP (CVE-2026-64893) and exposure of sensitive information through the debug interface (CVE-2026-64892). The fix is available in EC firmware V3.3b64 and CW firmware V3.3b26; HTTP has been disabled by default in the corrected version. INCIBE-CERT extends the scope to the EasyIO FG (end-of-life) and the FS-32. (ICSA-26-274-04, ICSA-26-274-05 — INCIBE-2026-691)
- VIVOTEK Camera Firmware (37 models): Unauthenticated OS command injection, CVSS score 10.0, and remote code execution with root privileges. CISA reports that a public proof-of-concept exists. Update to the latest firmware available in the VIVOTEK download center. (CVE-2026-22755 — ICSA-26-272-03, INCIBE-2026-676)
In closing
It is a heavy week in terms of volume, but the pattern matters more than the figure. ActiveMQ reappears within an access control system; Toptech exposes critical functions through its web interface; MikroTik and Moxa concentrate risk in administration interfaces. In all four cases, exposure grows when products that support physical operations remain connected to corporate networks without segmentation or strict management control.
The question for this week is concrete: which physical access systems, hydrocarbon terminals, routers, and gateways can be managed from unauthorized segments? If the answer is not available, it is advisable to start with an inventory of management interfaces, installed versions, and technical owners. This exercise allows for prioritizing updates and reducing the attack surface before a known vulnerability finds a path into operations.
The analysis and prioritization expressed in Perímetro are the editorial responsibility of Roberto Manzo. This publication does not replace specific technical advice for your organization.